Before You Patch. Why Patch Reliability Matters for Confident Deployment
Executive Summary Microsoft’s September 2026 security updates, KB5124008 and KB5124012, have been linked to USB audio failures on some Windows systems, highlighting the operational risk that can accompany security patching. Qualys TruRisk Eliminate classified both updates as Low Reliability, signaling the need for additional validation before production deployment. Patch Reliability helps IT and s
Read the brief →
Latest News
view all →
The vulnpocalypse rains iBugs down on Apple with record-setting number of patches
September Patch Tuesday part 2?

Acronis warns of actively exploited flaw in its cPanel backup plugin
Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild. [...]

Oracle September 2026 Critical Security Patch Update addresses 672 CVEs
Oracle addresses 672 CVEs in its September 2026 Critical Security Patch Update with 673 patches, including 104 critical updates. Key Takeaways The September 2026 Critical Security Patch Update (CSPU) contains fixes for 672 unique CVEs in 673 security updates 104 issues (15.5% of all patches) were assigned a critical severity rating Oracle E-Business Suite received the highest number of patches at

KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser extension on Google Chrome and

Iranian spies hit Windows machines with Chosen Brick data-stealing malware
'Enemies of the regime' on notice
Hackers target WordPress sites via third-party WooCommerce plugin
Hackers are actively exploiting a critical vulnerability in the WooCommerce Wholesale Lead Capture premium plugin for WordPress to upload a PHP backdoor. [...]
Most Firms Unable to Recover Quickly from Ransomware
Fenix24 found only four of more than 800 clients came close to stated ransomware recovery targets of 24-48 hours
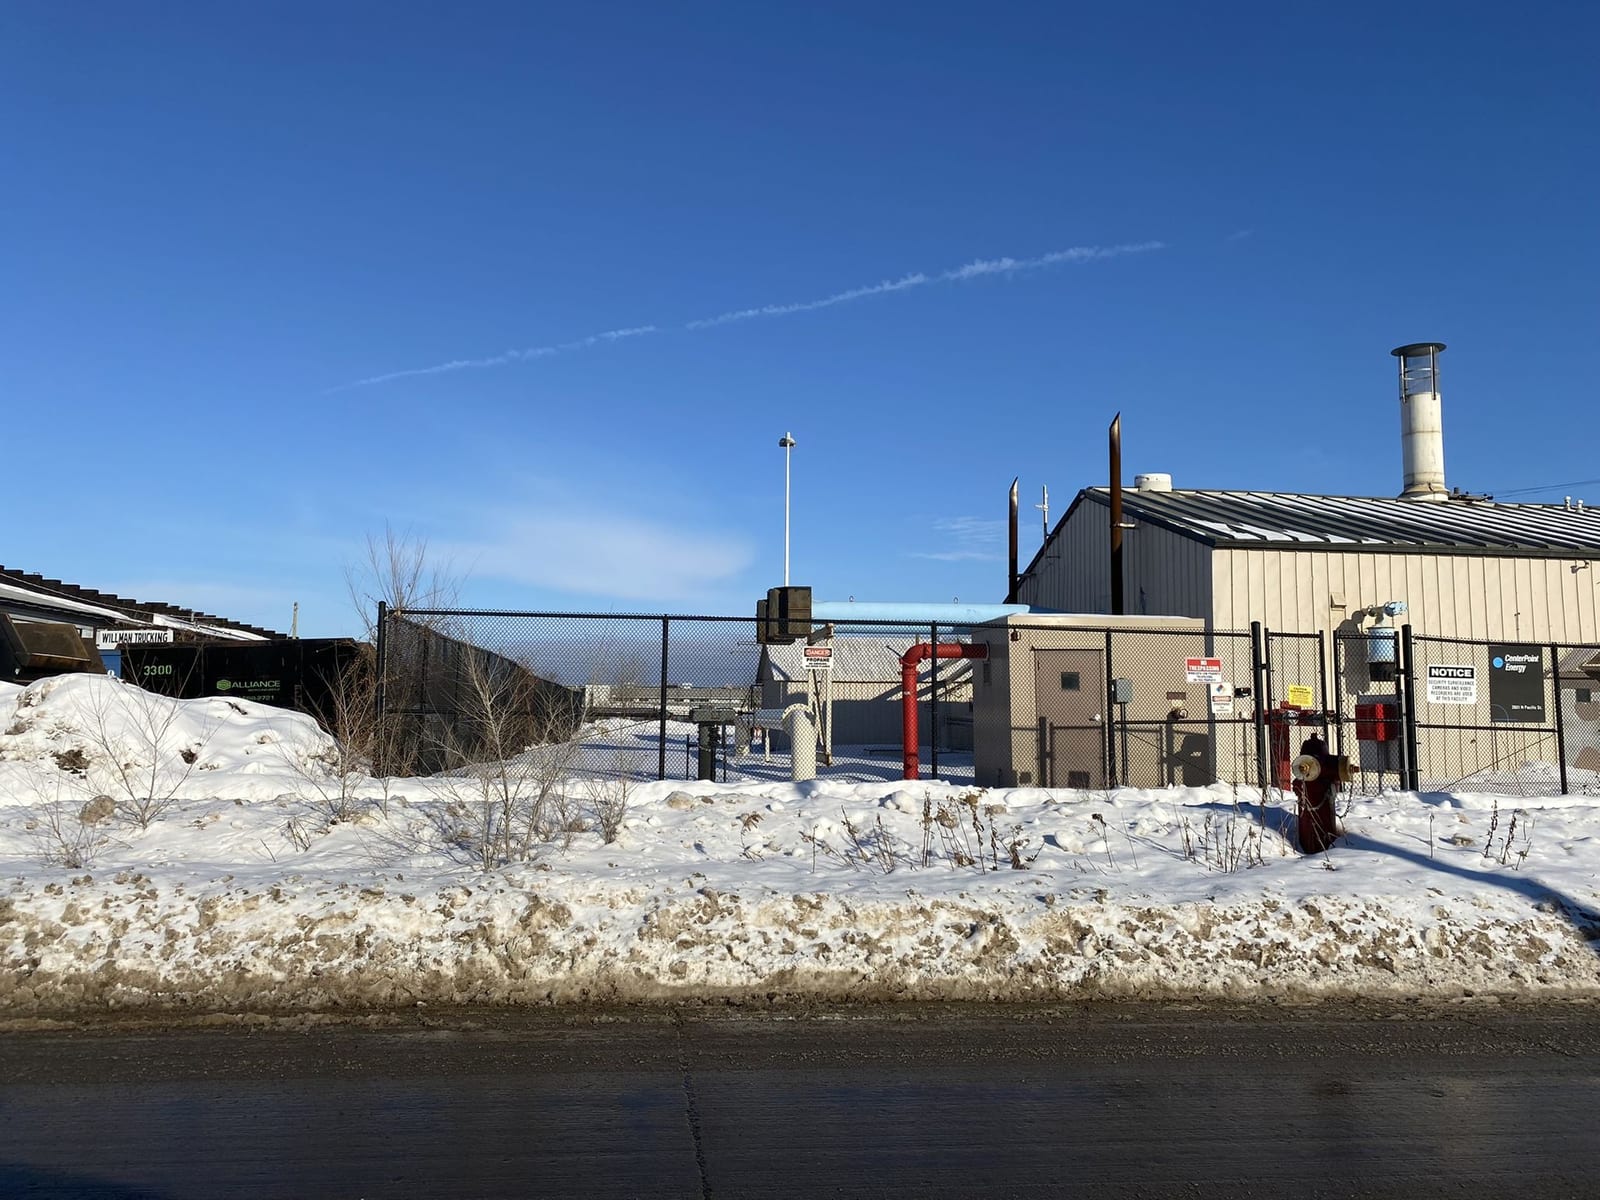
Electric and gas utility CenterPoint Energy warns of data breach after dark web post
Houston-based CenterPoint Energy notified federal regulators about an incident that exposed some customer data on the dark web.
Suspected Black Axe gang leaders face cybercrime charges in the US
Five alleged leaders of the Black Axe cybercrime syndicate, known for its involvement in global-scale cyber-enabled financial fraud, have been extradited to the United States to face wire fraud and money laundering charges. [...]
The Briefs
view all →
Meta AI builds detailed profiles of children from years of family posts
Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s inside man
Most chief audit executives can’t tell you what AI is worth yet
Supreme Court denies Trump request to allow USPS mail ballot changes
Exploited before disclosure
CVE tracker →vulnerabilities were called exploited by a KEV catalogue on or before the day they were published, in the last seven days, across 9 vendors. There was no patch window at all.
- CVE-2026-76461Cisco Secure Email Gatewaysame day3 of 3—
- CVE-2026-78006StellarWP the_events_calendarsame day1 of 30.78%
- CVE-2026-85706GitLab Community Edition and Enterprise Edition1d before3 of 311.1%
- CVE-2026-87827KGUARD_firmwaresame day1 of 31.1%
- CVE-2026-80099Newfold WP Plugin Websame day1 of 30.51%
- CVE-2026-14359YITH WooCommerce Waitlist Premiumsame day1 of 30.25%
- CVE-2026-87491Google Chromium V81d before3 of 30.86%
- CVE-2026-84869ConnectWise ScreenConnectsame day3 of 30.69%
2 more this week in the CVE tracker.
More Coverage
Maximum Severity GitLab Flaw Puts Supply Chains at Risk
New York Seizes a Dozen Celebrity Deepfake Websites
Hackers target exposed Vite dev servers to steal AWS, Azure secrets
Pro-Ukraine Hacking Cat group deploying new malware against Russian targets
CISOs Race to Control AI Agents Without Destroying Their Value
Hackers Exploit Maximum Severity Flaw in GitLab
Telus Warns Customers of Account Breaches
Certificate failures can cost firms over $250,000
AWS puts AI vulnerability detection to the test, and false positives pile up
Thorough reorganization at NSA will create five 'mission centers,' including cyber and AI
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 114
Hackers exploit Tencent app flaw to deploy GrayRabbit malware
Security Affairs newsletter Round 594 by Pierluigi Paganini – INTERNATIONAL EDITION
Anthropic CEO Dario Amodei Says AI Industry Needs to Give Safety Measures Time to Catch Up
GitLab CVE-2026-85706: One HTTP Request, No Authentication, Full File Read – Exploited Within 24 Hours
Security through obscurity is dead, and AI delivered the fatal blow
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data
Conti Hacker Who Built Malware and Attacked Victims Gets Four-Year Sentence
Week in review: Linux rootkit deployed on F5 BIG-IP APM devices, Cisco FMC bugs exploited